Showing posts with label Security Companies & Systems. Show all posts

Sunday, July 13, 2014

Russian Hackers Threatened Many Power Companies

The whole world has been threatened but currently the Power industry is more threatened by the hacker then world because the Power agencies have threatened by the Russian Hackers. There are many power companies in the United States and in Europe may be about to face power gone because a Russian Hacker group called “Energetic Bear” have attacked on these companies. This group has also known as Dragonfly is capable enough to disrupt any corporation because they have proper resources and size, suggested by the security company Symantec Corp.

They had posted that group is aiming to disrupt the main line of grid operators, petroleum operators, electricity generators and other important firms responsible for lighting up half of the world. The group is very active on web and becoming one of the largest attackers in the world. They are angry on govt. to use them for political strategies and there are many countries have been targeted including Spain, Serbia, Greece, Romania, Poland Turkey, Germany Italy and France.


“The group has a “nexus to the Russian Federation,” according to report published in January by Irvine, California-based CrowdStrike, which focuses on identifying web “adversaries.” The hackers also targeted academics globally, European governments, defense contractors and U.S. health-care providers, it said. Helsinki-based security firm F-Secure Oyj noticed the group’s focus shifting to industrial control systems earlier this year.” Lately Been Published on Site


There are Privacy Advocate trying to research on the matter for better knowledge, but it is still blur that the Govt. is involved or group is trying to sell to a government. In the most time the Hacker group is help full to common people as they have threaded the Brazilian Govt and FIFA to stop the huge money spending in the event on the other hand the people are starving.

Thursday, July 10, 2014

Privacy Advocates “American Intelligence Spying On own People is Hurts”


Companies thinks that their Data bases is very strong and they can’t get hacked but thing is NSA and FBI has some of the advanced technology that can be able to sneak around and spy on the servers looking for several information. Privacy advocates put allegation of Spying on NSA and also says that it conducting some surveillance program which is not good for the American Internet and consumers too. Bruce Schneier, cyber security experts said that NSA weakening the services that people use in daily life so that they can intercept the communication and also he put some light on a particular matter published on Reuters that NSA have giving about $10 Million to RSA to put some bugs into the technology so they can easily intercept the communication but RSA had said that they didn’t got any payment from NSA. He added that it is very poisonous to our Internet ecosystem the people have trust on.

“If the Chinese government had proposed to put in a backdoor into our computers and then paid a company $10 million to make that the standard we would be furious,” said Joe Hall, chief technologist at the Center for Democracy and Technology. “That’s exactly what the NSA has become: the best hacker in the entire world. While we cannot comment on specific, alleged intelligence-gathering activities.” Published on a site.

RSA is very prestigious security company and have invested many encryption techniques to tighten the security; recently RSA had revealed a Hack in Brazil, in which many people have faced a huge fraud case. Also the NSA is already got enough evidence about their surveillance programs, which lately have been revealed by the Edward Snowden. These incident have shaken the complete Internet and all companies, also makes them more aware about the NSA’s Security programs.

Friday, July 4, 2014

RSA Security Reports A Biggest Fraud In the History Revealed in Brazil

Recently, a Massie Cybercrime report from RSA Security had revealed that Internet Fraud malware had stole about $4 billion from a widely accepted payment system.  The RSA Security has did a research on the Fraud and posted a full report which stated that the “malware-based fraud ring” which had penetrated the online system called boleto, which misleading the payments to the bank accounts of the member of the ring. The boleto is widely used in Payment system, telephones, mortgage and credit card system. 

The report also says that the malware have altered about 500,000 transactions worth $4 billion dollars for about 2 year of the period. But still the researchers have unable to find out how many of those boleto’s were paid by actual owner of that transaction or they directly went to swindler. There were about 34 banks involved whose transaction were altered but did not mention any bank name. The federation of Brazilian bank that control everything in the country said the back have lost about $700 million in electronic transaction.

“This "Bolware" malware simply substitutes a different destination bank account on the form when it is being submitted online. The sender won't notice the change in a long string of numbers, and the intended recipient simply won't ever receive the money. Instead, it goes to the scammer's account — and the amount in such accounts, by RSA's estimates, exceeds $3 billion.”  As Published on a site


RSA said they have submitted report to the Brazil police and Federal Bureau of Investigation and to the federation. As Ask from the police they said they will examine the report and later will comment on it. This attack on the payment system is shackle the Economy or the country and also have very concerned about the security of the banks.

Thursday, June 19, 2014

Anti-Fraud Detection System Will Stop Worst Attacks On Computers


Ever wonder what if the hacker will stop and arrested before they could use any lethal technology to steal money, this is no that world but the new Company called Malwarebytes came into existence and launched a fraud prevention method called Anti Exploit. This system is for Windows Operating systems. This software is aims to protect the users of world’s most popular operating system by blocking-exploit technology which Malwarebytes acquired last year when they purchased ZeroVulnerabilitiesLabs. An survey reveals that over 1.3 billion user in the world uses Windows operating system every day but the problem is what Microsoft is doing to protect the user is not enough and several users have reported that they still getting hacked by phishing or with other techniques over the internet. The Free version of the Anti-Exploit is available and claims to protect the users from Internet security and listening on to user’s internet for any fraudulent activity, browsers, add-on will also be examine by the software. People can also buy a premium version of the Sioftware for $24 will also look on Microsoft Office PDF Media Players and other utilities.

“Businesses will want to invest in Anti-Exploit as an extra layer of protection against the kinds of attack methods central to the major hacks of late. Anti-Exploit is "not about the product. It's about the problem," Kleczynski said during an interview at Malwarebyte's office in San Jose, Calif. "Sometimes it catches the exploit so early we can't show the alert" that it has stopped an attack.” Read More at CNET


 The Windows Operating systems are bit low in Security policies, Users of the PC is very exhausted to have viruses and Malwares on the Computer and that’s why they can’t rely on it for any payment related work. Malwarebytes focus to keep the bad gys out of your system moto.

Monday, June 9, 2014

Another Fraud Activity of Govt. Has Revealed

It has been proved and Vodafone have also admits it that the Govt. operatives was working in its Exchange to snooping on the people of 29 countries. This fraud activity has been revealed by Law Enforcement Disclosure, says the world’s second largest telecommunication network the Govt. has asked them several times to intercepts or finds the secret information people conversation. The company has showed a 40,000 word of survey about the US authorities have been snooping around in the 29 countries with the help of Vodafone networks. Previously, US Telecom giant Verizon and AT&T have said same about their local surveillance program but this one is the biggest report of world surveillance program. US Govt. Security agency floating since Snowden showed their Work in bulk and recently he started a camping, in which he incorporated companies like Google, Microsoft to adding security option in websites and mobile apps.


Cnet Says “Vodafone identifies two different types of surveillance requests: lawful interception, and access to communications metadata such as phone numbers, addresses, times when calls were made, who the person called, and even the location of a phone to track the whereabouts of the subject.”

The main problem is our infrastructure and basic needs are not fully strong enough and technology is very old still in a large area of the planet, for example the companies in the world are using the IPv6 but there are still many countries that have not adopted it and still using the Internet Protocol Version 4. Vodafone report says the highest number of interception was made in Italy, where police were after Mafia and its kind of hard to tell that how many people have been compromised because there are thousands of people can be covered in a single request. Some countries have direct access to the network without even taking the permission from the court.

Tuesday, June 3, 2014

Interface Security Systems-Leading Provider of Internet Protocol Service Offers

Interface Security Systems, known as the portfolio business unit of SunTx Capital Partners has yesterday announced the completion of its massive notes offering worth $115 million by the help of its parent company named as Interface Master Holdings Internationals. Senior managers of this Security Company revealed that they would primarily use various proceeds of offering to fund the continued growth strategy of the company, which features national accounts space of different locations. This is a segment, in which the company has obtained unprecedented growth and development with the help of its unique IP i.e. Internet Protocol managed service offers.


Overview and Achievements of the Company

Interface Systems is responsible for providing wide range of security solutions, specifically, IP-based solutions for different types of retail marketplaces, small business units and commercial organizations. In addition, the company is responsible for the delivery of remote and interactive video surveillance solutions to different types of premises operating at the commercial level. Thus, whether you choose to visit in worldwide popular street markets, such as Camden Market, Spitafield Market, Covert Market and so on or to any famous shopping mall of United States and United Kingdom, you will expect to avail high level of security and surveillance solutions to assure protection of your life and property.


Until now, the company has achieved success in providing various types of physical security solutions, which include event or alarm monitoring services, interactive video surveillance solutions and life or fire safety systems. In addition, secured network services of the company will incorporate PCI compliant private level managed broadband services, managed digitized voice solutions and many other ancillary services powered by Internet Protocols.

In fact, the contribution of this company towards delivery of voice-based solutions definitely reminds us of the contribution of professionals working under an Israeli Company named Skylex. Technicians working under this company introduced Interactive Analytics voice-based solutions to apply in different contact center organizations. The main role of this technique is to allow for real-time indication of various emotional levels present in both agents and customers of call center units.

According to the statement given by Michael Shaw, “Interface is pleased to have closed on this Offering, which garnered significant interest from the investment community. Our unique ability to bundle physical security, video and digital voice over a PCI compliant private managed broadband network is changing the way multi-location retailers procure critical technology for their stores.” Readmore from here.  

Monday, May 26, 2014

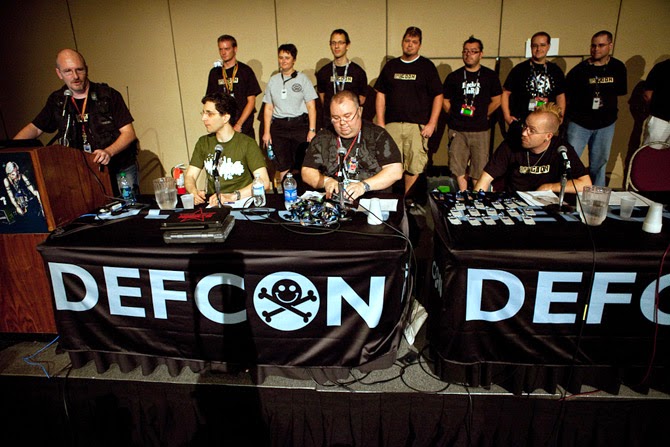
U.S Does Not Allowing Chinese People In Def Con conference At D.C

Washington D.C is restricting the Chinese nationals from attending the popular summer hacking conference in Las Vegas this year; this all come after the US accused Chinese hackers to hack the US govt. networks said a senior administrations official on Saturday. He also put some lights on the Washington could use the Visa restriction to keep them from attending the conference. Since people know that the summit is the only event where companies shows their technology innovation and other stuff another seminar called TEC Conference 2014, in which several tech leader will join the stage including Microsoft, Qualcomm, Nemesysco’s Amir Liberman and several other executives from the different nations. The Def Con is also a big event featuring the hackers from across the world and those are the black Hat hackers and US already accused the five Chinese hackers to hacking in the US military officers.


Reuters says “Organizers of the two conferences said they knew nothing about any efforts under consideration by Washington, but that they believed limiting participation from China was a bad idea. Jeff Moss, founder of both Def Con and Black Hat, could not be reached, although he posted his thoughts on Twitter: "First I have heard of it, boarding flight to D.C. now. I don't think it helps build positive community."
On the basis of US Accusations on China, United nation will not allow tham in the conference.At the event the employee of Chinese security software Maker Company Qihoo 360 will be delivering the keynote and will speak about the software vulnerabilities, while two scientists from Chinese Universities of Hong Kong are on talks with the hacking social media that Def con does not allowing any Chinese nationals to give any keynote or something. 

Wednesday, May 21, 2014

US Govt. Accuses Chinese Hacker Steal Trade Secrets by Compromising US Firms

The World has now threatened by hacker more than terrorists or anything else, as NSA was involved in several activity, in which they weren't supposed to be involved and people online security breach and data theft still was occurring, in the same manner the US Govt. accuses the Chinese hackers. The previous Mandiant reports that emphasize a new and advance security threat from China, a security company has released a full step by step video that shows how hacker can steal the information. Today the U.S Govt. announces a condemnation of unit 61398 indicating that the members of the hacking group, breach computers and stole the information from six victims, including a Chinese State owned company. The confrontation comes right after, when NSA has been accused to install unwanted software’s into the Servers that will be shipped to foreign customers.


USGovt. has said “Right about the time SolarWorld was rapidly losing its market share to Chinese competitors that were pricing exports well below costs, these hackers were stealing cost, pricing, and strategy information from Solar World’s computers. And while Westinghouse was negotiating with a Chinese state-owned enterprise over the construction of nuclear power plants, the hackers stole trade secret designs for components of those plants.”

The NSA had passing through bad time because it already accused to knowing the security bug Heartbleed but does not disclose it to take advantages, also the OpenDNS bug, which puts the internet to threat. The DOJ consider this act as a Crime, but sticky given that the now politely infamous NSA whistle blower Edward Snowden has directly accused the NSA has develop the industrial Surveillance that are responsible for collecting the Industrial Information such as  energy in Mexico, trade in Israel and oil in Venezuela.


Thursday, May 15, 2014

OpenDNS Has Got Funding From Cisco For Cloud-Based Enterprise Network Security


Cloud –based Network Company OpenDNS and also specialized to provides security services for Network, which is totally cloud based and help other companies to get their Networks safe from Hackers, has announced a $35 Million in series C funding from Greylock Partners, Sequoia Capital, Sutter Hill Ventures, Glynn Capital, Cisco, Evolution Equity, Lumia Capital, Mohr Davidow Ventures, and Northgate Capital. This new round has brought $53 million total funding until now. Open DNS has been found back in 2005 with the aim for customers to connect safely to the Internet. In Addition, the company has provide DNS controls along side with the parental and business filtration means give parents over controls about what their kids are doing on Internet. Also provides a way for consumer to hide their searched from ISP’s. After 2009 founder and CEO has see a new way to provide these services from companies too. The company has launched a security solution called Umbrella that protects the companies from hackers and their users regardless of where they work or what devices they use to access the internet.


TechCrunch says “The company has built out 22 data centers that had the ability to carry tremendous volumes of traffic needed by these enterprise companies. From a product standpoint, OpenDNS gives IT cloud-based software that monitors and secures every device that connects to a business’ network, from anywhere in the world and even for the devices that leave.”

The OpenDNS has 50 Million daily active users who use their services everyday and more than 10,000 enterprise customers using the security solutions. According to sources, company clients are biggest multinational corporations in the world like BP, H&R Block and Nvidia. Sales were also have grown to 100 percent and growing to other countries too.

Thursday, May 8, 2014

Hacker Targeted French Telco Orange Customers

France Telecom Services group Orange announced on Wednesday that they detected an data breach this week, professional Investigator says that about 1.3 million customer’s information been compromised including phone numbers, birth date, email addresses etc. The attack did not penetrate the payment system and no confidential information was stolen in the attack like credit card numbers. But Orange then sent out an email to warn their target customers having said that they may be again target with phishing pages to extract more confidential information like Credit card number or passwords. "The data recovered could be used to contact those concerned by email, SMS or by phone, particularly for phishing purposes," Orange said. This was the second data breach in just two months of time, when company trying to strengthen the defense against cyber attacks and bugs in Security Technology like Heartbleed bug.

Cnet says “Companies have been busy reinforcing their defenses in the wake of a massive security breach at US retailer Target and the revelation that the Heartbleed bug left unencrypted information available for the taking from web servers. The breach was detected April 18, but Orange said customer notification was delayed to allow for investigation and repair of the issue. Orange also reported in February that the personal information of about 800,000 of its customers was stolen in a similar attack in January. Both hacks came not long after Orange CEO Stephane Richard signed a charter in which the company pledged to protect its customers' personal data and respect their privacy.”

After hacking individuals for long time, hackers are now turning to tele communication companies for stealing the money or sensitive information like Credit card credentials and valuable information. The info which earn them money or cash.Also Vodafone Group announced that their 2 million users been compromised last year

Thursday, April 24, 2014

Apple Recorded $10.2 B Profit Out of $45.6B Revenue

The Investors are pretty much happy with Apple growth in Q2 of 2014 because they recorded huge Profit with $10.2 Billion out of $45.6 Billion revenue which is quite tough for the company with limited range of products. The sales of iPad were down to 16 percent. This revenue is above to both the $42 to $44 billion revenue from January and $43.6 billion last year. People loves Apple Technology that’s why Apple announced a seven-for-one split with $90 billion stock buy program. If we look on the products sale which sparks that revenue so there is only one product which thrust the sale is iPhone and said sold 43.7 million iPhones during the Quarter, more than the same quarter last year is 37.4 million. Also sold 16.3 million iPads, 4.1 million Macs, and 2.61 million iPods which is higher than 3.9 million Macs but lower than 19.5 million iPads.


The Verge Reported “We're very proud of our quarterly results, especially our strong iPhone sales and record revenue from services," Apple CEO Tim Cook said in a statement. "We're eagerly looking forward to introducing more new products and services that only Apple could bring to market. For its next quarter, which ends in June, Apple said it expects to bring in between $36 to $38 billion in revenue, which is up from the $35.3 billion it made during the same quarter a year ago, though lower than the $38.3 billion Wall Street forecasted”


Apple considers as innovative companies and it also shows that people with iPhones and iPad are classy and don’t care about money, that’s why people love to buy the Apple products and specially iPhone and the recently found Heartbleed bug apple patches the bug firstly because of their concern about customer security.

Saturday, April 19, 2014

Heartbleed Security Bug Was Used To By Pass The Past Multifactor Authentication


It’s not been a long time since the Heartbleed bug introduced the world and created a whole lot of mess in the tech world and then it was flood of leaks of new founding related to the bug and here is another founding that the with such flaw hackers could be able to breach the Virtual private network or could bypass the verification of information in multi factor or two step verification. The Report comes from the privacy company Mandiant says in the initial stages of bug, it could be possible that a hacker exploits the VPN, which is known as the most secured network till now. 


Cnet Says “In bypassing multifactor authentication, the attackers were able to get around one of the stricter methods of ensuring that someone is who they say they are. Instead of just a single password, multifactor authentication requires at least two of three kinds of credentials: something you know, something you have, and something you are.While much of the Internet discussion of Heartbleed has focused on attackers taking advantage of the vulnerability to steal private encryption keys, Glyer said the attack against the unnamed Mandiant client indicates that session hijacking is also a risk.”


Companies like Facebook, Google, Microsoft and other’s released a note saying that they have solved the security bug but urge to change the usernames and passwords. The vulnerability was introduced inadvertently several year ago in the OpenSSL, which is the mostly used encryption technique by two third of the internet but wasn't disclosed till this year and since then firms are struggling to patch the exploit in their servers. This was the biggest privacy breach in internet history and almost all firms were vulnerable to this threat but wasn't aware of it.

Tuesday, April 1, 2014

IBM battle With Bharti Airtel To Save $2.5 Billion

Last month IBM India has fired a dozen of Top to mid level executives with other Human resources who accused of the fraud. The fraud was the outsourcing contract of about $2 billion outsourcing with Bharti Airtel and a subordinated company which was founded by Former IBM-ers. The agreement signed back in 2004 which stated to manage the telecom Networks, desktop application and software’s at Airtel. It will cost about $300 million annually and $2 billion for all IBM India. As of now Airtel has to renew this contract and share of IBM has diluted down to $100 million yearly. So the whole matter is little bit messed up and executives from both side created a fraud type situation.
TechCrunch published “IBM and Airtel are now negotiating terms of a contract that could be reduced to around 3-4 years with total value of less than $400 million, The Bharti contract renewal has already undergone over a dozen iterations; it was supposed to get signed and announced weeks ago. Ongoing investigations into ‘unprofessional conduct’ of some IBM-ers and customer staff has made it a contract everybody wants to sign, but with conditions that reflect lack of trust, The specific charge being leveled internally is called the business conduct guideline violation.At least a quarter of all the work being outsourced to IBM was being subcontracted to Mara-ISON, and the motives look questionable,”

Several Companies like Yahoo, Google, and Facebook are defining the rules and regulations for their employees to maintain transparency with executives and company so that situation like this cannot be created. IBM already suffers from Low revenue in India that’s why they fired 2500 employee last year. So as contract bounds IBM not to take any independent subcontract or purchase any hardware and software solution but board of directors from both side will decide what product to acquire and how.

Wednesday, March 26, 2014

Yahoo’s Boosts Up The Security To Tumblr

It’s been just a matter of time when Yahoo Acquired Tumblr, which gave a lot of panic to its billion users to their blog security but Yahoo, took care of it and boost up the services by adding SSL into the service, which was not by default but user has to into the setting to activate it. Adding more juice to the Service with its two step verification service like Gmail means every time when a user tries to login they send an one-time-password to the user’s phone, which will expire in 5 minutes if not entered. Tumblr has Google and Facebook like reputation in the tech industry in terms of security concerns. This news comes out after Tumblr made a blog post, which hold off the outside hackers to get access to the blogs dashboard. The two factor’s work like one key is your password and other company will send you when you login to the blog.


Tumblr wrote “The smile of a loved one, your childhood blanket. A handsome bodyguard to take you in his arms, “Security” can mean a lot of things in this crazy life, but nothing says “security” like Tumblr’s two-factor authentication. It’s available as an option in your Settings page as of right now. You know how you need two keys to launch a nuclear missile? Two-factor authentication works like that. One key is your password, the other key is your cellular phone, and you need both to access your Tumblr Dashboard. Keep your Dashboard safe and secure, like you do with your nuclear missile.”


The goal is to makes hard to hack and nobody except user can get into the blog. The Two Factor authentication did it well with precision. The Big hacker is to worry about is Government sneaksinto people’s life or spying so this could stop them from sneaking around.

Saturday, March 15, 2014

The NSA Responds To Assertion It Masquerade as Facebook And Infected PCs With Malware

Two Days ago when Edward Snowden Made his Latest appearance at South by Southwest Festival, where he was invited by ACLU itself to talk about the Mass collection of User specific data and privacy over internet. Recently, Facebook CEO made a post on his Facebook Page about the calling to Obama to stop this Matter. These all news were drawing US government attention towards to answer such difficult Security questions, so NSA has responded in kind and published an explanation on their official website. The base of all accusation are, Of course Documents leaked by Whistleblower Edward Snowden, which is another over reach from NSA, if Snowden choose to stay in US he would have been in a jail but agency got shocked in past year by a constant documents leaking by Snowden and choose to go to Russia.


NSA made their comments “Recent media reports that allege NSA has infected millions of computers around the world with malware, and that NSA is impersonating U.S. social media or other websites, are inaccurate. NSA uses its technical capabilities only to support lawful and appropriate foreign intelligence operations, all of which must be carried out in strict accordance with its authorities. Technical capability must be understood within the legal, policy, and operational context within which the capability must be employed.”


The NSA denied about the story about infectingMillions of computers and also that Mark Zuckerberg publically posted an angry note on his facebook page to call to President over the matter. He was pointed out that it was his company that the documents mention as masquerade as party which very tough to listen. Regarding to the claim that NSA impersonate the websites, because the new were saying that in some ways NSA masqueraded as a Fake Facebook Server, using Facebook as a launched pad to their malware.


Tuesday, March 11, 2014

Snowden Addresses The SXSW Conference And Criticizes NSA Again

Today at SXSW conference, NSA whistleblower Edward Snowden joined the event via Video conferencing to speak on Mass surveillance, Security and Online Privacy. The video was showed in Russia to Austin, Texas and whole world from Google Hangouts through seven proxies. Snowden speaks on countless subjects about Government spying, as he also answered the answered several questions from Twitter. Firstly he Pointed on Intelligence agencies should follow “law enforcement” model of defense, which means they have to cease the mass collection of user instead only go for suspects with a warrant. The same agenda is also suggested by congress members including Senators Rand Paul and Ron Wyden. He also pointed out on James clapper lie to congress incident about bulk collection of data and later on when the member of Intelligence Committee rushed to defend him, and accused Government of “cheerleading the NSA instead of holding them accountable”


Snowden Said “We need a watchdog that watches congress,the closest thing being proposed by both congress and President Barack Obama is a so-called “public advocate”. The proposed role would litigate against the NSA when agents go to the secret Foreign Intelligence Surveillance Court, to ask for permission to spy on Americans.eroding our protections of communications to get an attack advantage, the NSA is harming the integrity of the Internet itself, a field in which the United States has a global advantage in terms of innovation. Using an analogy of a vault”


The main issue is the tech industry, is the ability to show how much data did Government ask or affected by NSA spying, then only every single person will be able to know the exact number of user that NSA sneak into. Recently several Tech companies releases the Transparency Report, which can be a bit more informative if they disclose the user full information, but with that so called report we still don’t know exactly which agency are collecting data.


Thursday, March 6, 2014

Speek Raises $5.1 Million Series A Funding To Change Old-Fashioned Conference Calling Solutions

Speek, a conference calling and voice solution startup, which initially providing online tools which enable user to switch or jump on different calls without worrying about, what device you have on your hand? Than do additional activity on calls once connected. Last week company announces $5.1 million Series A investment. The investment comes from 500 Startups, Edward Norton, CNF investments, Middleland Capital, and others. The other members in round are Michael Chasen, Timothy Chi and Sonny Ganguly, Jeffery and Robert Wolf and others and Alexander Pessala from Middleland will be joining the board. Speek was founded in 2012 by John Bracken, co-founder of Evite and co-founder C T O Danny Boice based in Washington D.C and were knew the pain to dealing with Conference calling.
Danny Boice had said in a interview “Speek updates the old system by, first, making it easier to join a call. Every Speek users gets their own personal link – for example, Boice has speek.com/danny. These can be distributed to others instead of a dial-in, and callers can choose to join the conference in a number of ways, depending on what’s easier for them. They connect using VoIP from their web browser, enter in their own phone number to have the service ring them, or, if on mobile, they can basically just hit a button to join the call from the Speek app.”
Speek is offering a Freemium solution, with $10 per month a user and recently launched new service called “Speek For Teams” on number of user can communicate together. Generally this solution works well for companies with 10 to 100 employees. With this funding, they’re planning to add more feature to the “Speek for Teams” and other services. Features like Security Controls, Collaboration editing a Document, tools to share Slideshows.

here is the Google Hangout with Founder

Monday, March 3, 2014

Report Says: UK Spy Agency Collected Webcam Images From Yahoo Users With The Help Of NSA

In another dramatic exposure about the digital Intelligence from NSA and US Security agency, Reports says that British surveillance agency GCHQ had started a program in 2008 and 2012, which collected photos from Yahoo Chat messenger user’s webcams. The Project was intended to collect a huge amount of Webcam photos, including Sex Content from more than 1.8 million Yahoo users in period of 6 month across the world. The project was called “Optic Nerve” project was detailed into the GCHQ documents which is exposed by NSA contractor Edward Snowden. Reports also claimed that the NSA got profit from the project, and research helped them to identify the activity of Users on Yahoo Messenger. Users didn’t even know that they were targeted by US Government, targeted not for any particular reason.
Guardianpublished a full report “Programs like Optic Nerve, which collect information in bulk from largely anonymous user IDs, are unable to filter out information from UK or US citizens. Unlike the NSA, GCHQ is not required by UK law to "minimize", or remove, domestic citizens' information from its databases. However, additional legal authorizations are required before analysts can search for the data of individuals likely to be in the British Isles at the time of the search. There are no such legal safeguards for searches on people believed to be in the US or the other allied "Five Eyes" nations – Australia, New Zealand and Canada. GCHQ insists all of its activities are necessary, proportionate, and in accordance with UK law.”


As for Yahoo, they powerfully denies any previous information about the existence of the program, Reports are coming out every day but no one taking any precautions to violation of its customers privacy. Yahoo and some other tech companies have asked for more transparency from government surveillance about what data they don’t want on the servers.


Wednesday, February 26, 2014

MasterCard to boost credit card security with Smartphone’s

MasterCard, the biggest Credit Card based company, concerned about the security on Smartphone, with hacks, Stolen Credit Card, identity theft so with such Frauds most of the companies looking for the better security options. Master Card announced on this Monday that they will partnered with the Mobile technology firm Syniverse to provide more security for people, who take all transaction on their phone. Firm this move is bit different because they will the users geo location, when the user is on the move. The concept is a credit card can too be used unless it is within in the range of user’s phone. For example, if user is in California and Card is swiped in Canada, the transaction will not be performed. It happens much time when user uses their card in other countries without telling bank about their traveling. The Geo Location feature will be helpful in this case.


Hany Fam MasterCardpresident of Global Strategic Alliances said “This collaboration of two global technology leaders opens up a whole new range of possibilities for end users, ensuring a seamless payment and mobile experience. By leveraging the speed and intelligence of our global network and combining it with Geo location solutions, we are enabling your MasterCard to uniquely work where you and your phone are, anywhere in the world. With nearly 2 billion MasterCard cards in circulation, the world’s most advanced payments technology company is processing 65,000 transactions every minute, while Syniverse currently reaches more than 5 billion mobile devices globally via 1,000 mobile service providers.”


MasterCard collaborated with Syniverse to Make Phone wallets, which is a evolving technology from past few years. As enterprises know that Smartphone’s are future so they want to offer user to pay for purchased item from their android phone or iPhone only. Last year three major firms MasterCard, Visa and American Express had partnered to develop a digital Payment system by which they can increase the security using token method.


Tuesday, February 18, 2014

Cybereason Reveals Its Malicious Ops Detection Platform


The Main Focus of the security industry is fraud detection as it happens or prevents a hacker to break the security. Cybereason, a security startup setup by former Israeli intelligence agency members, they just commercialize their Enterprise. It is a quarrel between so many enterprises that security attack or spying on people is unexpected, company working on the technology by which one could track all step by step attack strategy of the hacker, this could lead companies to overcome the vulnerabilities in their websites. Cybereason has developed a pro-active security platform for enterprises to constantly observe system with the goal of spot hacker activities and objective, if they prepare for stole the data heist, and enable businesses to cut off the hacker before anything happen. 

Firms VP MarkTaber said “In the movies you might see somebody breaking in and then shortly thereafter running out with [corporate secrets]. But in reality there’s a long process and a whole bunch of different actions and things that these attackers are doing one they’re inside, This sort of sophistication, up until a couple of years ago, was only at the nation state level, was not at the enterprise. But now it’s really coming into the enterprise. And unfortunately enterprises are not very well equipped to discover these sorts of hacking operations as all of their skills; all of their money is on the prevention side. Malware can be a part of a malicious operation [but] we’re really looking at a series of things that a hacker or hacking operation would do to accomplish their end goal”

Mark gives an example of a malicious attack in progress that they exposed on its beta users—A anonymous huge media firm—was the event where an unknown software had installed on many users computers and then frequently used for remotely switch on the camera and microphone on computers, So many investors looking forward to invest in such innovative organization. 

here is the video which will explain that How hacking works??